


The Underestimated Attack Surface
How to Secure OT Maintenance Access Points
Maintenance, remote access, and engineering are part of everyday life in modern production environments. However, every instance of necessary access to machines and systems simultaneously expands the attack surface. This article highlights where risks hide and how companies can protect themselves.
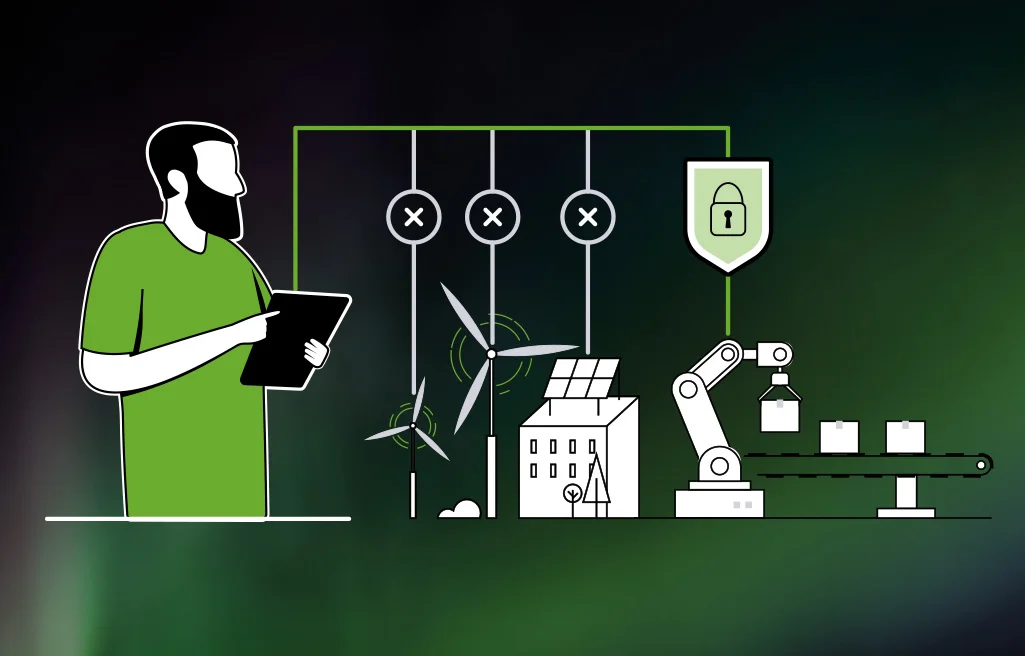
Maintenance access to machines and systems is indispensable in manufacturing companies today: Service technicians must configure control systems, equipment manufacturers need access for maintenance work, and internal engineering teams must be able to transfer programs to the various PLCs.
Consequently, critical systems can be accessed through maintenance access points. At the same time, these access points often come with extensive permissions. In addition, there are many different users who need access to the respective machines and systems. It is precisely this combination that makes maintenance access points an attractive target for cyberattacks.
Maintenance access points require protection
There are several typical scenarios involving maintenance access points that significantly increase the risk of a successful attack:
- Shared accounts: Where multiple technicians use the same account, it is impossible to track who made which changes. There is also a risk that login credentials will be shared, and the company will lose track of who has access to them.
- Uncontrolled remote access: Although remote access connections are encrypted, there is no control over where the access originates or who is establishing the connection. Anyone with the login credentials can access the systems without further verification.
- Extensive permissions: Although a service provider is only supposed to maintain one motor in the machine, they are granted access to the entire production facility. If this access is breached, an attacker could potentially move through the network and reach other systems.
- Directly accessible OT systems: If control systems or other components can be accessed directly via the internet, it is not possible to establish controlled connections.
These various risks demonstrate that an effective security strategy requires a combination of network architecture, access management, and secure connections. With the Endian Secure Digital Platform, companies can implement such a security strategy using a single solution. The following steps are important:
- Isolate access points from control systems
A key security consideration for OT is to isolate maintenance access points from control systems. Rather than granting direct access to control systems, a security gateway should be deployed upstream as a controlling interface. Security gateways are equipped with multiple security features that provide a significantly enhanced level of protection: A firewall controls which connections are permitted. For example, users can specify from which country access is permitted. Network zones can be set up to determine which systems within the company are allowed to communicate with one another. An IDS/IPS continuously monitors communication to detect and block any malware at an early stage. - Implement centrally controlled access
Companies need to know which individuals accessed the systems, when they did so, and what actions they performed there.
The Endian Secure Digital Platform enables centralized role- and permission-based management. The Endian Switchboard is the central management tool that allows to manage users, devices, and permissions. This makes it easy to implement principle of least privilege: each user is granted only the permissions necessary to perform their tasks. Strong authentication is also crucial for remote access. Multi-factor authentication makes it more difficult for attackers to gain direct access to OT systems using stolen usernames and passwords. Additionally, it is possible to require prior approval for every access request and to document remote maintenance sessions via video recording. - Protecting Connections
Once users have been uniquely identified and their permissions have been clarified, the connection between the end device and the OT environment remains another critical component of the security architecture. During remote maintenance and engineering access, in particular, sensitive data and control commands must be securely transmitted between the user’s end device and the remote OT systems.
The Endian Connect app establishes a secure tunnel between the user’s endpoint and the remote resources. With native support for Windows and macOS, users can access remote resources from their preferred devices.
Conclusion
Maintenance and engineering access points are essential for the operation of modern production facilities, but they also represent a potential vulnerability. Effective protection is achieved through a combination of network architecture, access management, and secure connections.
Do you need help securing your maintenance access points?

How attackers get in across Europe
ENISA Threat Landscape 2025
A maintenance access point offers exactly what attackers look for: valid credentials and a reachable system. ENISA analysed how attacks in the EU begin. The two most common routes lead straight there.
Source: ENISA Threat Landscape 2025, 4,875 incidents analysed in the EU, July 2024 to June 2025, figures rounded
of attacks started with phishing, the most common route to valid credentials
started with the exploitation of a vulnerability, often on reachable system
of attacks were launched via botnets